Critical Software Testing Course
About our
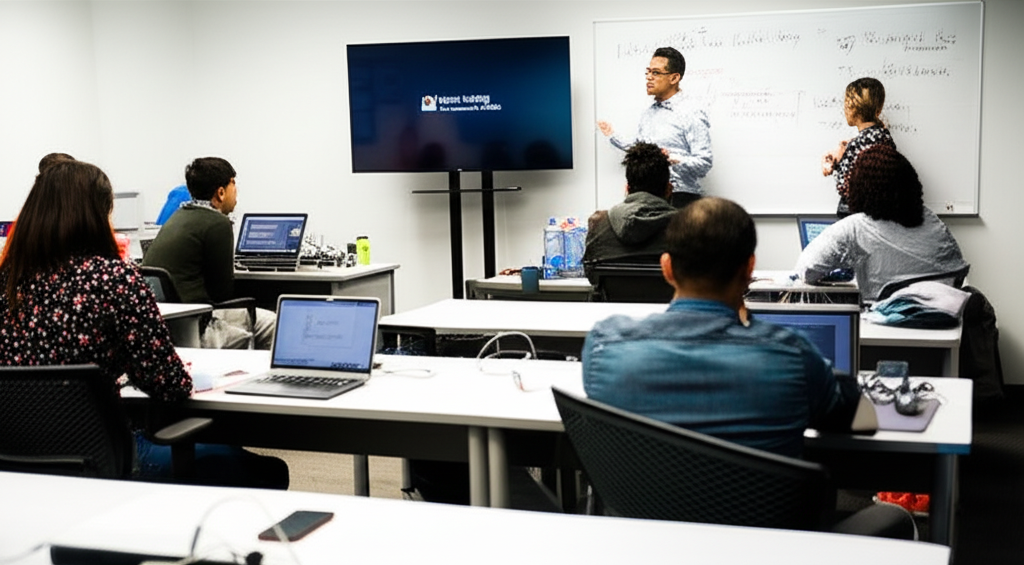
The Critical Software Testing Course focuses on rigorous practices for verifying and validating software systems operating in demanding environments, such as the aerospace, automotive, and medical industries. It delves into methodologies such as model-based testing, black-box and white-box testing, and static and dynamic analysis techniques, essential for detecting and mitigating errors that could compromise system security and reliability. Emphasis is placed on compliance with standards such as DO-178C, ISO 26262, and IEC 62304. The course provides skills in the use of test management, automation, and code analysis tools, including the creation and execution of test cases, code coverage analysis, and defect management. Participants are prepared for roles such as software test engineers, quality analysts, and test team leaders, equipping them with the necessary skills to ensure quality and security in the development of critical software, contributing to the prevention of failures and risks.
Critical Software Testing Course
- Format: Hybrid
- Duration: 3 months
- Hours: 300 H
- Language: English / Spanish
- Registration date: 23-10-2026
- Start date: 12-12-2026
- Available places: 3
799 $
Competencies and results
What you will learn
1. Advanced Testing for Critical Software: Techniques and Strategies
- Master rigorous verification and validation methods for mission-critical software.
- Apply static testing techniques, including code review and static analysis.
- Design and execute dynamic tests, such as unit, integration, and system tests.
- Implement white-box, black-box, and gray-box testing.
- Utilize specialized tools for testing mission-critical software, such as simulators and emulators.
- Analyze and manage test coverage, including code coverage and decision coverage.
- Apply error and defect management techniques in the context of mission-critical software.
- Understand and apply industry standards for testing mission-critical software (DO-178C, IEC 61508, etc.).
- Develop and maintain comprehensive test plans and traceability documentation.
- Implement test automation strategies to increase efficiency and repeatability.
2. Comprehensive Evaluation of Critical Software: Practical and In-Depth Learning
- Master methodologies for the comprehensive evaluation of critical software.
- Apply advanced static and dynamic analysis techniques.
- Implement white-box and black-box testing for code verification.
- Identify and mitigate security vulnerabilities in software.
- Utilize static and dynamic code analysis tools.
- Understand and apply secure development standards (ISO 26262, DO-178C).
- Manage the critical software lifecycle, from design to maintenance.
- Perform performance and stress tests to ensure software robustness.
- Analyze and understand functional security requirements.
- Develop effective test plans and test cases.
3. Comprehensive user-oriented design and validation (from modeling to manufacturing)
You will learn to integrate the entire product development process, from initial model conception to final validation, applying user-centered methodologies. You will develop skills in parametric design, ergonomics, simulation, sustainable materials, 3D visualization, and manufacturing management, ensuring efficient, safe solutions that meet current industry standards.
4. Critical Software Testing: Design, Execution and Analysis
4. Critical Software Testing: Design, Execution, and Analysis
Designing tests for critical systems, considering security and reliability requirements.
Executing comprehensive tests, including unit, integration, and system tests.
Analyzing test results, identifying failures, errors, and vulnerabilities.
Implementing risk-based testing methodologies and industry standards.
Using automated testing tools and static and dynamic analysis techniques.
Evaluating test coverage and the effectiveness of test cases.
Applying test management techniques, including planning, monitoring, and reporting.
Knowledge of relevant standards and regulations for critical software testing.
Proficiency in performance and security testing, including penetration testing.
1. Quality Assurance in Critical Software: A Comprehensive Approach
- Master the fundamental principles of quality management in mission-critical software development.
- Apply quality methodologies and standards specific to the aerospace and defense industry.
- Identify and mitigate risks inherent in the development of highly reliable software.
- Implement comprehensive verification and validation techniques, including unit, integration, and system testing.
- Utilize static and dynamic analysis tools and techniques to ensure code quality.
- Manage configurations and control versions of mission-critical software.
- Understand certification and regulatory compliance requirements for mission-critical software (e.g., DO-178C).
- Develop skills for managing mission-critical software projects, including planning, monitoring, and control.
- Analyze case studies and best practices in mission-critical software quality assurance.
- Learn to Conduct effective quality audits and code reviews.
6. Validation and Verification of Critical Software: Methodologies and Tools
6. Validation and Verification of Critical Software: Methodologies and Tools
- Understand the principles of validation and verification (V&V) of critical software.
- Identify the different types of critical software and their specific requirements.
- Explore V&V methodologies, including static and dynamic testing.
- Use V&V tools for code analysis, unit testing, integration testing, and system testing.
- Apply configuration management and change control techniques to critical software.
- Ensure compliance with relevant regulations and standards for critical software (e.g., DO-178C, IEC 61508).
- Develop and execute comprehensive V&V plans.
- Analyze the risks and mitigations associated with critical software.
- Evaluate the security and reliability of the software.
- Apply best practices for documentation and traceability in V&V.
Who this program is for:
Critical Software Testing Course
- Engineers with degrees in Aerospace Engineering, Mechanical Engineering, Industrial Engineering, Automation Engineering, or related disciplines.
- Professionals working in rotorcraft/eVTOL OEMs, Maintenance, Repair, and Overhaul (MRO) Organizations, consulting firms, or technology centers.
- Specialists in Flight Testing, certification, avionics, control systems, and flight dynamics who wish to deepen their knowledge.
- Representatives of regulatory bodies and Authorities, as well as professionals involved in Urban Air Mobility (UAM) and eVTOL projects, who seek to acquire skills in regulatory compliance.
Recommendations: Prior knowledge in areas such as aerodynamics, control systems, and structures is suggested. A B2+/C1 level of English or Spanish is required. We have bridging tracks available to address any gaps in knowledge.
- Standards-driven curriculum: you will work with CS-27/CS-29, DO-160, DO-178C/DO-254, ARP4754A/ARP4761, ADS-33E-PRF from the first module.
- Accreditable laboratories (EN ISO/IEC 17025) with rotor bench, EMC/Lightning pre-compliance, HIL/SIL, vibrations/acoustics.
- Evidence-oriented TFM: safety case, test plan, compliance dossierand operational limits.
- Mentored by industry: teachers with experience in rotorcraft, tiltrotor, eVTOL/UAM and flight test.
- Flexible modality (hybrid/online), international cohorts and support from SEIUM Career Services.
- Ethics and security: safety-by-design approach, cyber-OT, DIH and compliance as pillars.
1. Introduction to Critical Software Testing: Importance and Challenges
2. Fundamental Principles of Testing: Design, Execution, and Analysis
3. Critical Testing Strategies: White Box, Black Box, and Gray Box
4. Levels of Testing: Unit, Integration, System, and Acceptance
5. Test Design: Techniques and Methods
6. Configuration Management and Change Control
7. Testing Tools: Selection and Application
8. Documentation in Critical Testing: Plans, Test Cases, and Reports
9. Standards and Regulations: Compliance and Compliance
10. Case Studies: Best Practices and Lessons Learned
2.2 Strategic Planning of the Evaluation
2.2 Definition of Evaluation Criteria
2.3 Selection and Adaptation of Evaluation Techniques
2.4 Practical Implementation of the Techniques
2.5 Data Collection and Analysis
2.6 Interpretation of Results and Report Preparation
2.7 Evaluation of the Coverage and Depth of the Tests
2.8 Identification and Prioritization of Defects
2.9 Security Considerations in the Evaluation
2.20 Continuous Improvement of the Evaluation Process
3.3 Fundamentals of Testing in Critical Software
3.2 Applicable Types of Tests
3.3 Designing Effective Test Cases
3.4 Test Execution and Data Collection
3.5 Results Analysis and Failure Reporting
3.6 Coverage and Evaluation Metrics
3.7 Testing Tools in Critical Software
3.8 Regression and Maintenance Testing
3.9 Continuous Integration and Automated Testing
3.30 Practical Applications and Case Studies
4.4 Test Planning and Design
4.2 Test Execution: Techniques and Tools
4.3 Results Analysis and Defect Reporting
4.4 White Box Testing: Design and Application
4.5 Black Box Testing: Strategies and Examples
4.6 Integration and System Testing
4.7 Test Configuration Management
4.8 Test Automation: Introduction and Benefits
4.9 Test Metrics and Coverage Assessment
4.40 Best Practices and Case Studies
5.5 Advanced Testing Techniques: Design and Application
5.5 Testing Strategies: Selection and Adaptation
5.3 Test Coverage: Metrics and Optimization
5.4 Model-Based Testing: Implementation and Benefits
5.5 Security Testing: Vulnerabilities and Mitigation
5.6 Performance Testing: Stability and Scalability
5.7 Advanced Testing Tools: Selection and Use
5.8 Test Automation: Design and Execution
5.9 Test Results Analysis: Interpretation and Reporting
5.50 Case Studies: Application in Critical Software
5.5 Requirements Evaluation: Analysis and Validation
5.5 Software Architecture: Review and Evaluation
5.3 Detailed Design: Inspection and Verification
5.4 Implementation: Unit and Integration Testing
5.5 System Testing: Functionality and Performance
5.6 Acceptance Testing: Criteria and Execution
5.7 Risk Management: Identification and Mitigation
5.8 Root Cause Analysis: Problem Solving
5.9 Evaluation Reports: Documentation and Communication
5.50 Case Studies: Real-World Experiences
3.5 Testing Fundamentals: Principles and Types
3.5 Testing Lifecycle: Planning and Execution
3.3 Test Design: Techniques and Strategies
3.4 Test Execution: Procedures and Control
3.5 Defect Management: Reporting and Tracking
3.6 Regression Testing: Automation and Optimization
3.7 Black Box Testing: Techniques and Application
3.8 White Box Testing: Techniques and Application
3.9 Results Analysis: Metrics and Evaluation
3.50 Practical Examples: Application in Critical Software
4.5 Test Design: Requirements-Based Design
4.5 Test Execution: Implementation and Control
4.3 Results Analysis: Interpretation and Evaluation
4.4 Test Planning: Strategies and Timelines
4.5 Test Cases: Creation and Management
4.6 Traceability Matrices: Requirements and Tests
4.7 Unit Testing: Test-Driven Development
4.8 Integration Testing: Strategies and Techniques
4.9 System Testing: Scenarios and Use Cases
4.50 Test Reports: Documentation and Communication
5.5 Quality Concepts: Definition and Standards
5.5 Quality Planning: Strategies and Processes
5.3 Quality Assurance: Activities and Controls
5.4 Quality Control: Inspection and Testing
5.5 Defect Management: Lifecycle and Resolution
5.6 Quality Metrics: Measurement and Analysis
5.7 Quality Audits: Types and Execution
5.8 Continuous Improvement: PDCA Cycle and Models
5.9 Configuration Management: Change Control
5.50 Quality Certifications: Standards and Requirements
6.5 Validation: Process and Activities
6.5 Verification: Process and Activities
6.3 Validation Methodologies: Approaches and Techniques
6.4 Verification Methodologies: Approaches and Techniques
6.5 Validation Tools: Selection and Use
6.6 Verification Tools: Selection and Use
6.7 Code Review: Techniques and Tools
6.8 Static Analysis: Tools and Application
6.9 Traceability: Requirements and Testing
6.50 Case Studies: Validation and Verification
7.5 Requirements Analysis: Review and Evaluation
7.5 Design Analysis: Architecture Evaluation
7.3 Code Analysis: Review and Metrics
7.4 Quality Assurance: Activities and Controls
7.5 Risk Management: Identification and Mitigation
7.6 Defect Management: Lifecycle and Resolution
7.7 Quality Metrics: Measurement and Analysis
7.8 Quality Audits: Types and Execution
7.9 Continuous Improvement: PDCA Cycle and Models
7.50 Integration with Development: Processes and Tools
8.5 Testing Methodologies: Selection and Application
8.5 Functional Testing: Techniques and Strategies
8.3 Non-Functional Testing: Performance and Security
8.4 Regression Testing: Automation and Optimization
8.5 Acceptance Testing: Criteria and Execution
8.6 Test Design: Techniques and Tools
8.7 Test Execution: Procedures and Control
8.8 Defect Management: Reporting and Follow-up
8.9 Test Automation: Strategies and Tools
8.50 Best Practices: Standards and Recommendations
6.6 Principles of Verification and Validation of Critical Software
6.2 Validation Methods: Review, Static and Dynamic Analysis
6.3 Software Verification: Unit, Integration, and System Testing
6.4 Requirements and Design Validation
6.5 Verification and Validation Tools
6.6 Test Design for Critical Software
6.7 Case Studies: Practical Applications of V&V
6.8 Configuration Management and Change Control
6.9 V&V Documentation and Reporting
6.60 Industry Standards and Regulatory Compliance
- Hands-on methodology: test-before-you-trust, design reviews, failure analysis, compliance evidence.
- Software (depending on licenses/partners): MATLAB/Simulink, Python (NumPy/SciPy), OpenVSP, SU2/OpenFOAM, Nastran/Abaqus, AMESim/Modelica, acoustics tools, planning toolchains DO-178C.
- SEIUM Laboratories: scale rotor bench, vibrations/acoustics, EMC/Lightning pre-compliance, HIL/SIL for AFCS, data acquisition with strain gauging.
- Standards and compliance: EN 9100, 17025, ISO 27001, GDPR.
Capstone-type projects
- Advanced Testing: Test case design, automation, coverage and vulnerability analysis.
- Validation/Verification: Planning, requirements, regression testing, risk management.
- Quality Assurance: Audits, metrics, continuous improvement, standards (DO-178C).
- Software Analysis: Code review, static testing, defect analysis.
- Advanced Testing: Strategies in Critical Software.
- SIL/HIL Validation: Evaluation of Embedded Systems.
- Quality Assurance: Assurance in Critical Software.
- DO-178C: Compliance and Verification.
- Critical Testing: Design and execution of comprehensive testing, results analysis, and code optimization.
- SIL/HIL Validation: Implementation of validation and verification tests, ensuring software robustness.
- Quality Assurance: Application of methodologies to ensure system quality and reliability.
- DO-178C: Regulatory compliance, test plan, and documentation for aeronautical software.
“`html
- Advanced Testing: Test case design and automation for critical software.
- Comprehensive Validation: Application of V&V methodologies in complex projects.
- Domain Testing: Implementation of risk-based testing strategies.
- Efficient Testing: Execution and analysis of results, defect reporting.
Quality Assurance: Implementation of assurance processes and tools.
“
Admissions, fees, and scholarships
- Profile: Background in Computer Engineering, Mathematics, Statistics, or related fields; practical experience in NLP and valued information retrieval systems.
- Documentation: Updated CV, academic transcript, SOP/statement of purpose, project examples or code (optional).
- Process: Application → Technical evaluation of profile and experience → Technical interview → Review of case studies → Final decision → Enrollment.
- Fees:
- Single payment: 10% discount.
- Payment in 3 installments: No fees; 30% upon registration + 2 equal monthly payments of the remaining 35%.
Monthly payment: available with a 7% commission on the total; annual review.
Scholarships: based on academic merit, financial need, and promoting inclusion; agreements with companies in the sector for partial or full scholarships.
See “Calendar & Calls for Applications,” “Scholarships & Grants,” and “Fees & Financing” in the SEIUM mega-menu.
Do you have any questions?
Our team is ready to help you. Contact us, and we will respond as soon as possible.
F. A. Q
Frequently asked questions
Yes, we have international certification
Yes: experimental models, real data, applied simulations, professional environments, real case studies.
It is not mandatory. We offer leveling tracks and tutoring.
Completely. It covers e-propulsion, integration, and emerging regulations (SC-VTOL).
Recommended. There are also internal challenges and consortiums.
Yes. Online/hybrid modality with planned labs and visa support (see “Visa & Residence”).